Carmine Valente Joins the FAIR Institute Board: Another Lov-a-FAIR Story


Some people need a few dates before they fall for FAIR. For Carmine Valente, it was love at first quantification.
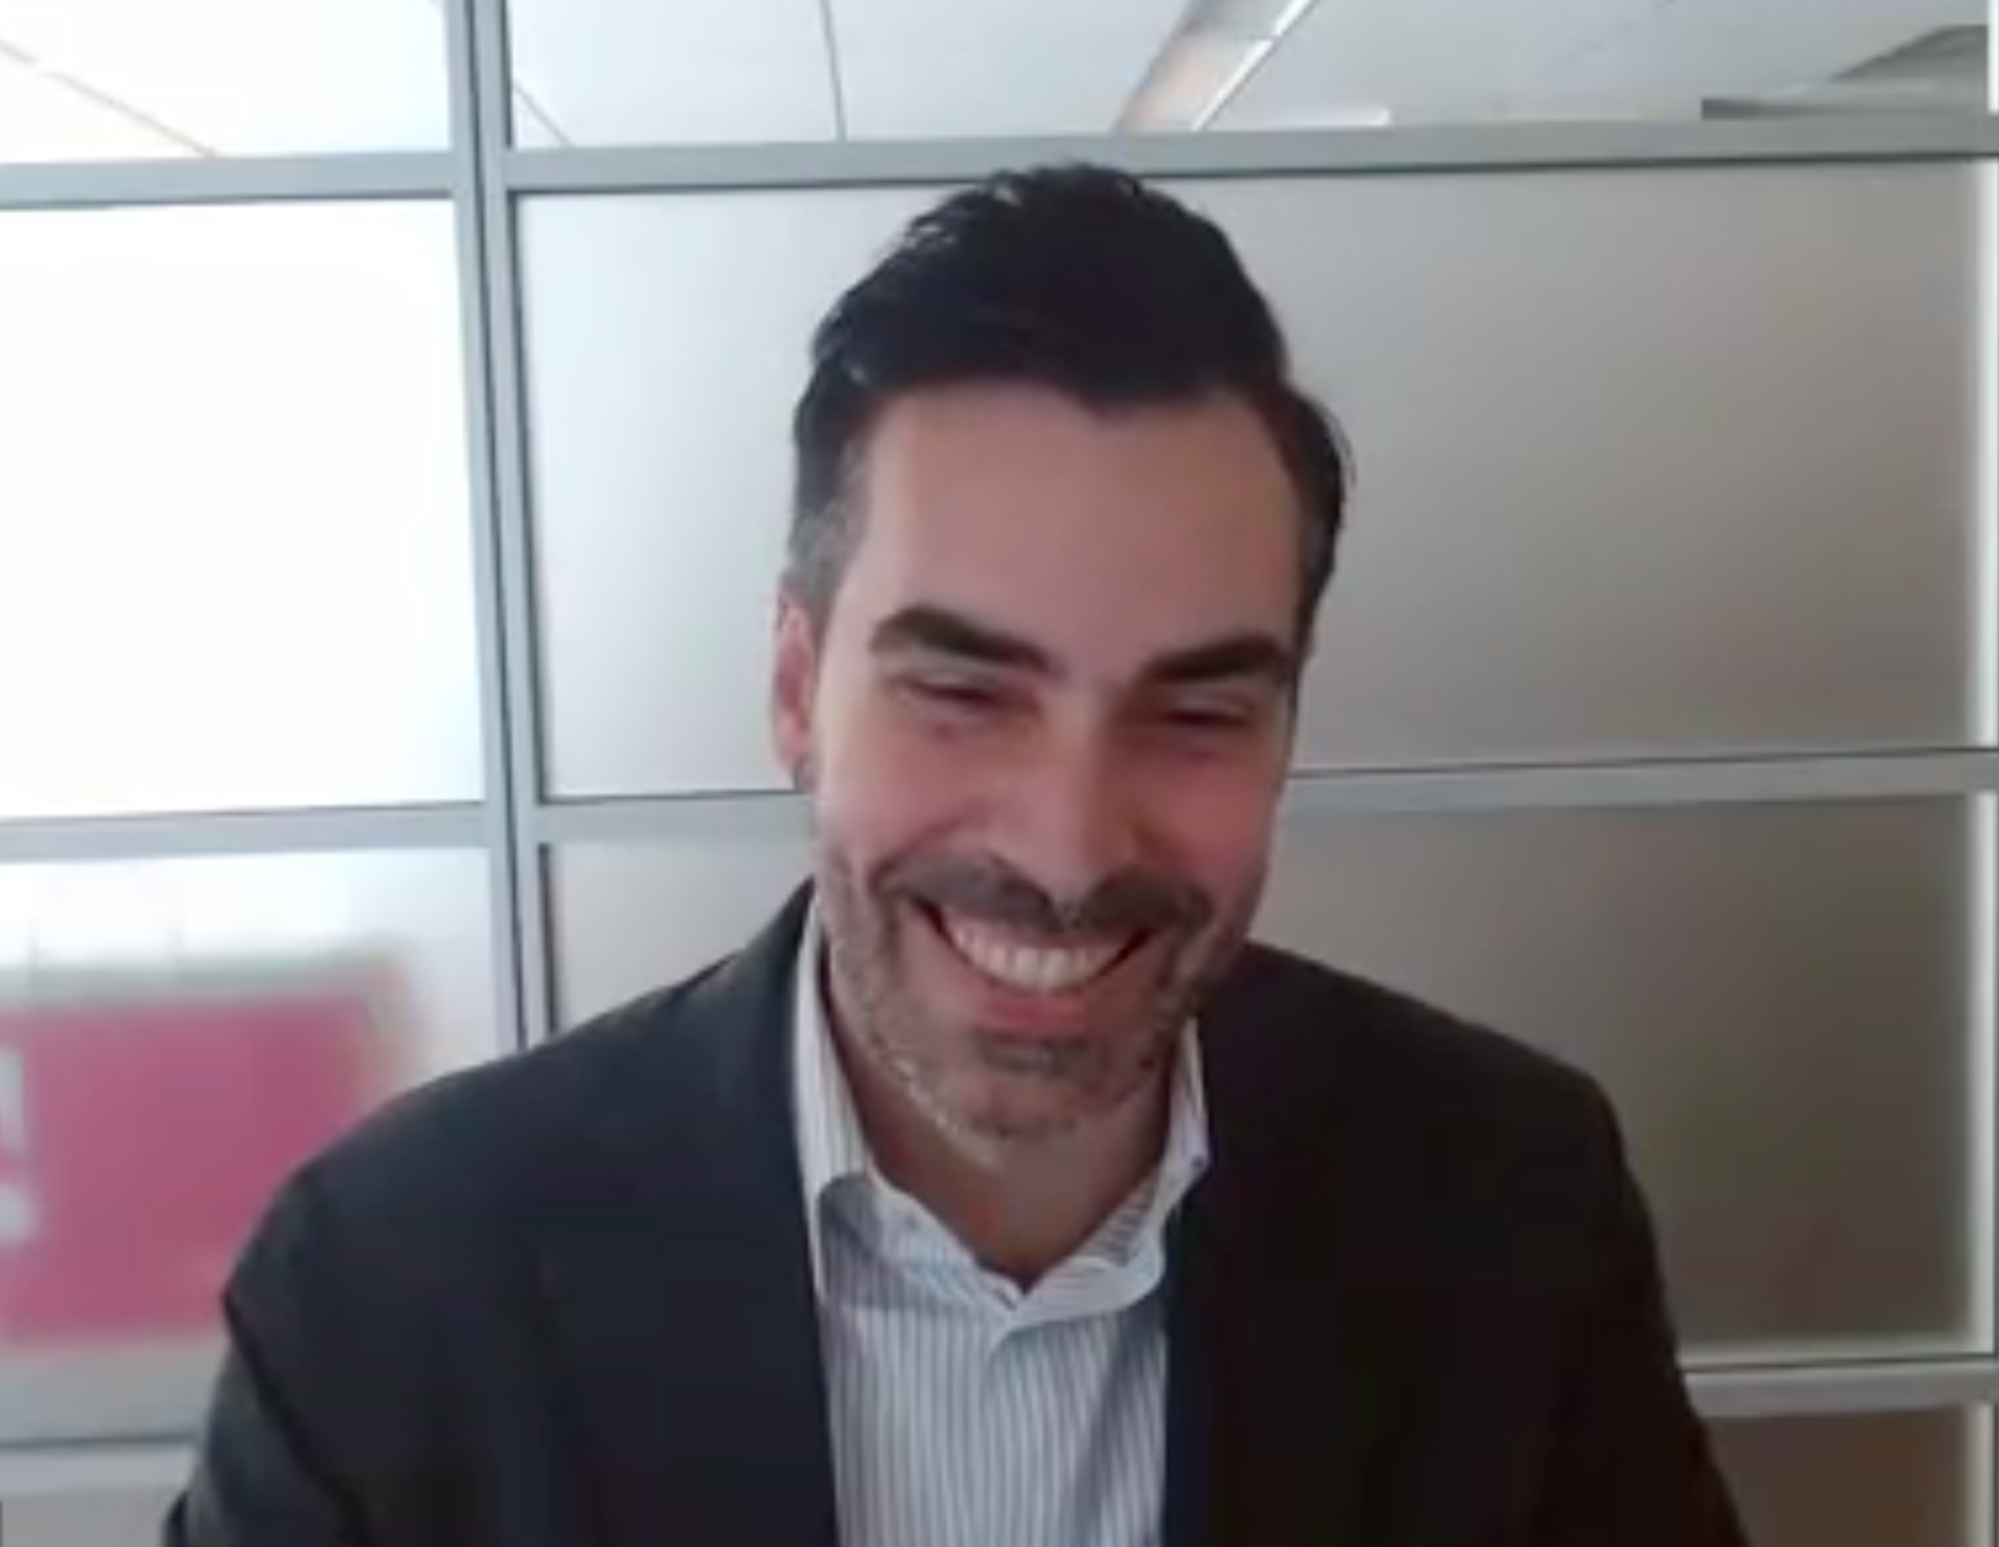
The FAIR Institute is delighted to welcome Carmine Valente, Deputy CISO at ConEdison, to its Board of Directors. Carmine led the cybersecurity risk program at Paramount and helped build EY's cybersecurity practice, with a career that has taken him from Europe to Africa to the U.S.
We sat down with Carmine to hear his lov-a-FAIR story. Here is our conversation, with small edits for readability.
The meet-cute: a board that needed a better story
FAIR Institute: Every great lov-a-FAIR starts somewhere. When did you first cross paths with FAIR? Was it love at first quantification, or did it take a few dates to win you over?
Carmine Valente: It was definitely love at first quantification. My first encounter with FAIR was at Paramount, where, among other things, I led the cybersecurity risk program. We were looking for better ways to communicate risk to our board, our leadership and our business stakeholders, something I had struggled with in the past.
I started talking with peers and partners, and FAIR came up as a way to quantify risk. When I looked into it, I realized almost immediately that it was one of the few truly practical ways to quantify risk and explain it in terms the business understands very well, and the board does too.
The road to here: from code to three continents
FAIR Institute: Walk us through the career journey that brought you here. What were the defining turns, and maybe a detour or two, that shaped how you think about risk?
Carmine Valente: I started the way most technologists do, as a developer, and then moved into analysis. The first turning point was SAP. Anyone who has worked with SAP knows it brings you very close to the business. That's where I first gained real insight into business risk and how the business looks at things.
From there, I was lucky enough to join EY just as it was building its cybersecurity practice. Those of us who helped build cybersecurity programs from scratch developed a risk perspective along the way, and most of my career since has been in the risk space.
The other turning point was international exposure. At EY, I had the chance to work in Africa, which eventually opened the door to the U.S. That gave me a very different perspective on how risk is seen across industries and regions, in Europe versus the U.S. versus Africa. My passion for risk is something I developed over time.
Making it official: from CISO to Chief Information Resilience Officer
FAIR Institute: Plenty of people admire FAIR from afar. What made you decide to put a ring on it and join the Institute's Board, and what do you hope to bring to the relationship?
Carmine Valente: I've long been convinced that the CISO role would evolve into a CIRO, a Chief Information Risk Officer. Today I think it will still be a CIRO, but more likely a Chief Information Resilience Officer, and risk plays a critical role in resilience.
Look at where the industry is heading: new technologies, AI and frontier AI, and a geopolitical situation where new risks are popping up everywhere. If you can't quantify those risks and explain them in a way your business partners clearly understand, you're only doing half of the job.
That's what gave me the push to get more involved. I believe FAIR will play a critical role in the broader transformation of risk, and in how CISOs talk about risk with their partners, their boards and their executive leadership.
Happily ever after: FAIR as the language of risk
FAIR Institute: Fast-forward five years. How do you hope our industry will have evolved in the way it understands and manages risk, and what role should FAIR and the Institute play in getting there?
Carmine Valente: I'm a strong believer that FAIR will play a critical role in the future of cyber, whether it stays "cyber" or becomes cyber resilience or something else. It took a couple of decades to build our know-how in cybersecurity. We have the skills and the knowledge. Now we have to get much better at communicating risk.
In the CISO community, we keep saying that cybersecurity is for everybody, not just for cybersecurity people. But I always remind my team: if we can't explain cybersecurity to everybody else, they won't care about it, and they won't take action.
My hope is that FAIR positions itself as the leader in becoming that language, the protocol between cyber and the business, the board and leadership. It should explain what's happening, what could go wrong and what we can do to make it better. I'm very confident this will become reality. Every day, as cyber professionals, we'll have to explain why we need certain measures and why the business should change how it looks at things. To do that, we'll need to communicate what changed.
Welcome to the family, Carmine
Carmine joins the Board at a pivotal moment for the Institute as we build the next chapter of our mission. His path from developer to risk leader, his experience building cybersecurity programs from scratch, and his perspective across Europe, Africa and the U.S. will help us make FAIR the common language between cyber and the business.
Want to hear more about where the Institute is headed? Join us for FAIR Forward, our virtual event on November 10, 2026, where we'll unveil the strategy for FAIR Institute 2.0.
Please join us in welcoming Carmine to the FAIR Institute Board of Directors. Love at first quantification, indeed.